Altered | HackTheBox
A hard-difficulty Linux box centered on a Laravel password-reset flow brute-forced past rate limiting with spoofed IP headers, then a type-juggling bypass that unlocks SQL …
Read More →In-depth research and notes on security technologies, tradecraft, and lab write-ups.
A hard-difficulty Linux box centered on a Laravel password-reset flow brute-forced past rate limiting with spoofed IP headers, then a type-juggling bypass that unlocks SQL …
Read More →
An easy-difficulty Linux box chaining an insecure password reset into admin access, an LFI that becomes RCE through Apache log poisoning, lateral movement by abusing BSD r-services …
Read More →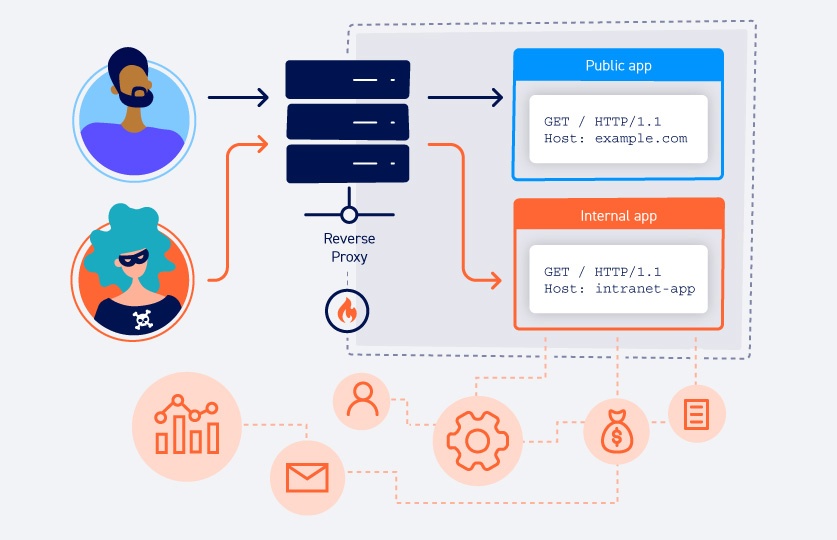
This post talks about how the Host header becomes an SSRF primitive, how front-end routing works, why trusting the Host header breaks the trust boundary between proxy and back-end, …
Read More →
A full breakdown of XML External Entity (XXE) injection: what it is, the XML internals that make it possible, where the attack surface hides, and a few examples of attack paths. …
Read More →
An easy-difficulty Linux box centered on a blind SQL injection in a registration form's country parameter, chained through sqlmap's FILE privilege abuse into a PHP webshell and …
Read More →
A hard-difficulty Windows AD box built around a cross-forest MSSQL trusted link, SeServiceLogonRight abuse to recover SeImpersonatePrivilege, and unconstrained TGT delegation …
Read More →
My write-up for the skills assessment of HTB Academy's DACL Attacks I module. Starting from a low-priv foothold, we chain a targeted Kerberoast, two separate WriteOwner/GenericAll …
Read More →
A web challenge centered on an AI 'Auto-mod copilot' that runs raw GraphQL queries on behalf of chat users with a privileged service account, allowing anyone to promote themselves …
Read More →
A Linux box centered on PostgreSQL. Superuser database access leads to RCE inside a Docker container, ident protocol leaks a username, and docker group membership hands over root …
Read More →
A Linux box built around eXtplorer, a PHP file manager. Default creds get a webshell, leaked credentials pivot to a local user, and disk group membership leads straight to root.
Read More →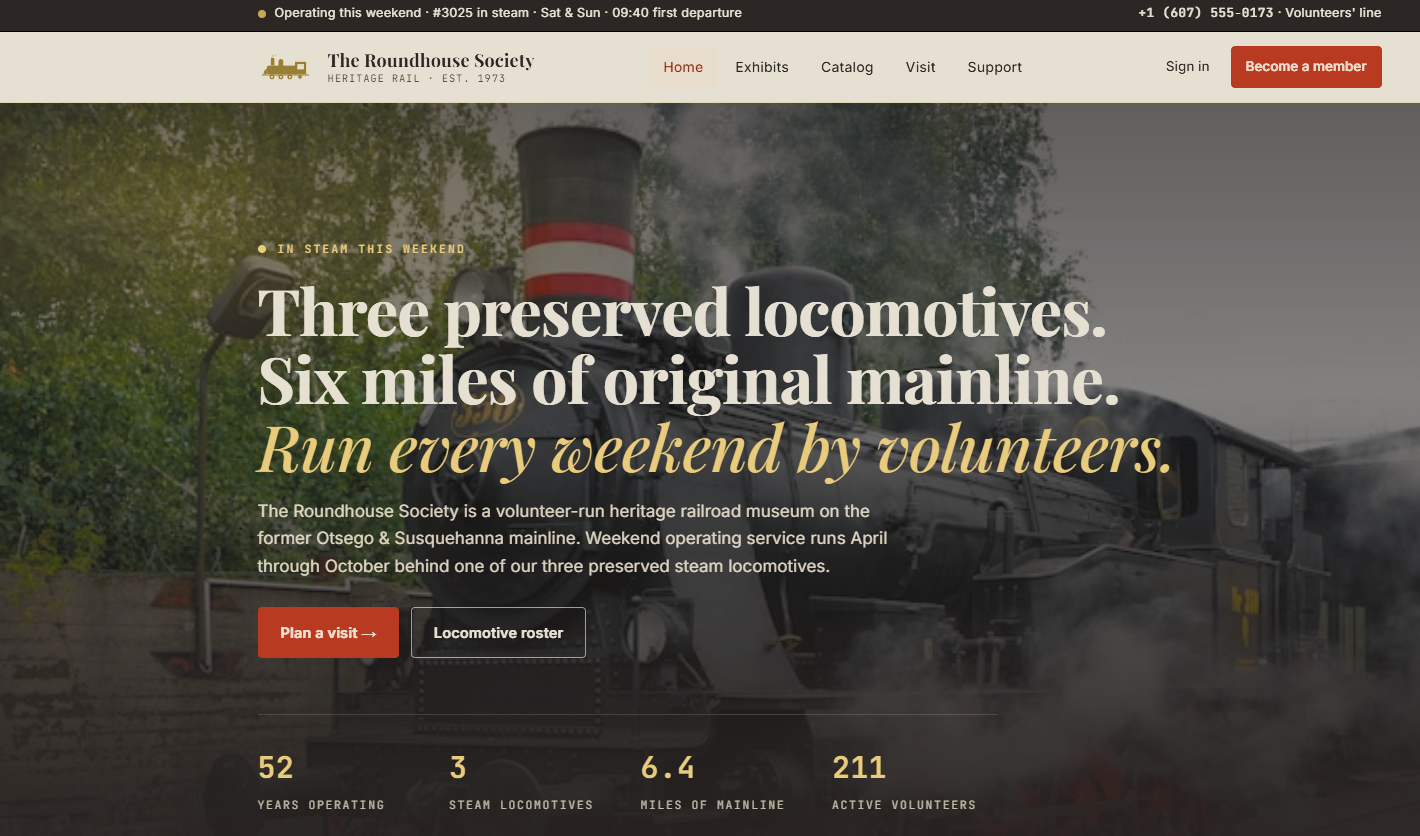
A web challenge involving Reflected DOM XSS in a museum catalog application, escalated to authenticated credential harvesting via same-origin fetch.
Read More →
An easy Windows box running Umbraco CMS. Creds leak from a world-readable NFS share, an authenticated Umbraco exploit gets a foothold, and a Print Spooler abuse gets SYSTEM.
Read More →
A walkthrough of GroundWorm, a hard-rated DFIR Sherlock on HackTheBox, tracing a simulated APT attack from initial access through ransomware deployment using Splunk and API …
Read More →
An investigation into a simple infostealer, following the retired TeleStealer Lab from CyberDefenders, covering static and dynamic malware analysis.
Read More →
A high-level overview of the steps taken in the MalaCrypt lab from CyberDefenders, covering static and dynamic malware analysis.
Read More →
A walk-through of the Linux Privilege Escalation room in the Jr Penetration Tester pathway on TryHackMe, covering eight core privilege escalation techniques.
Read More →